DNV expanded audit covers all Silverstream sites
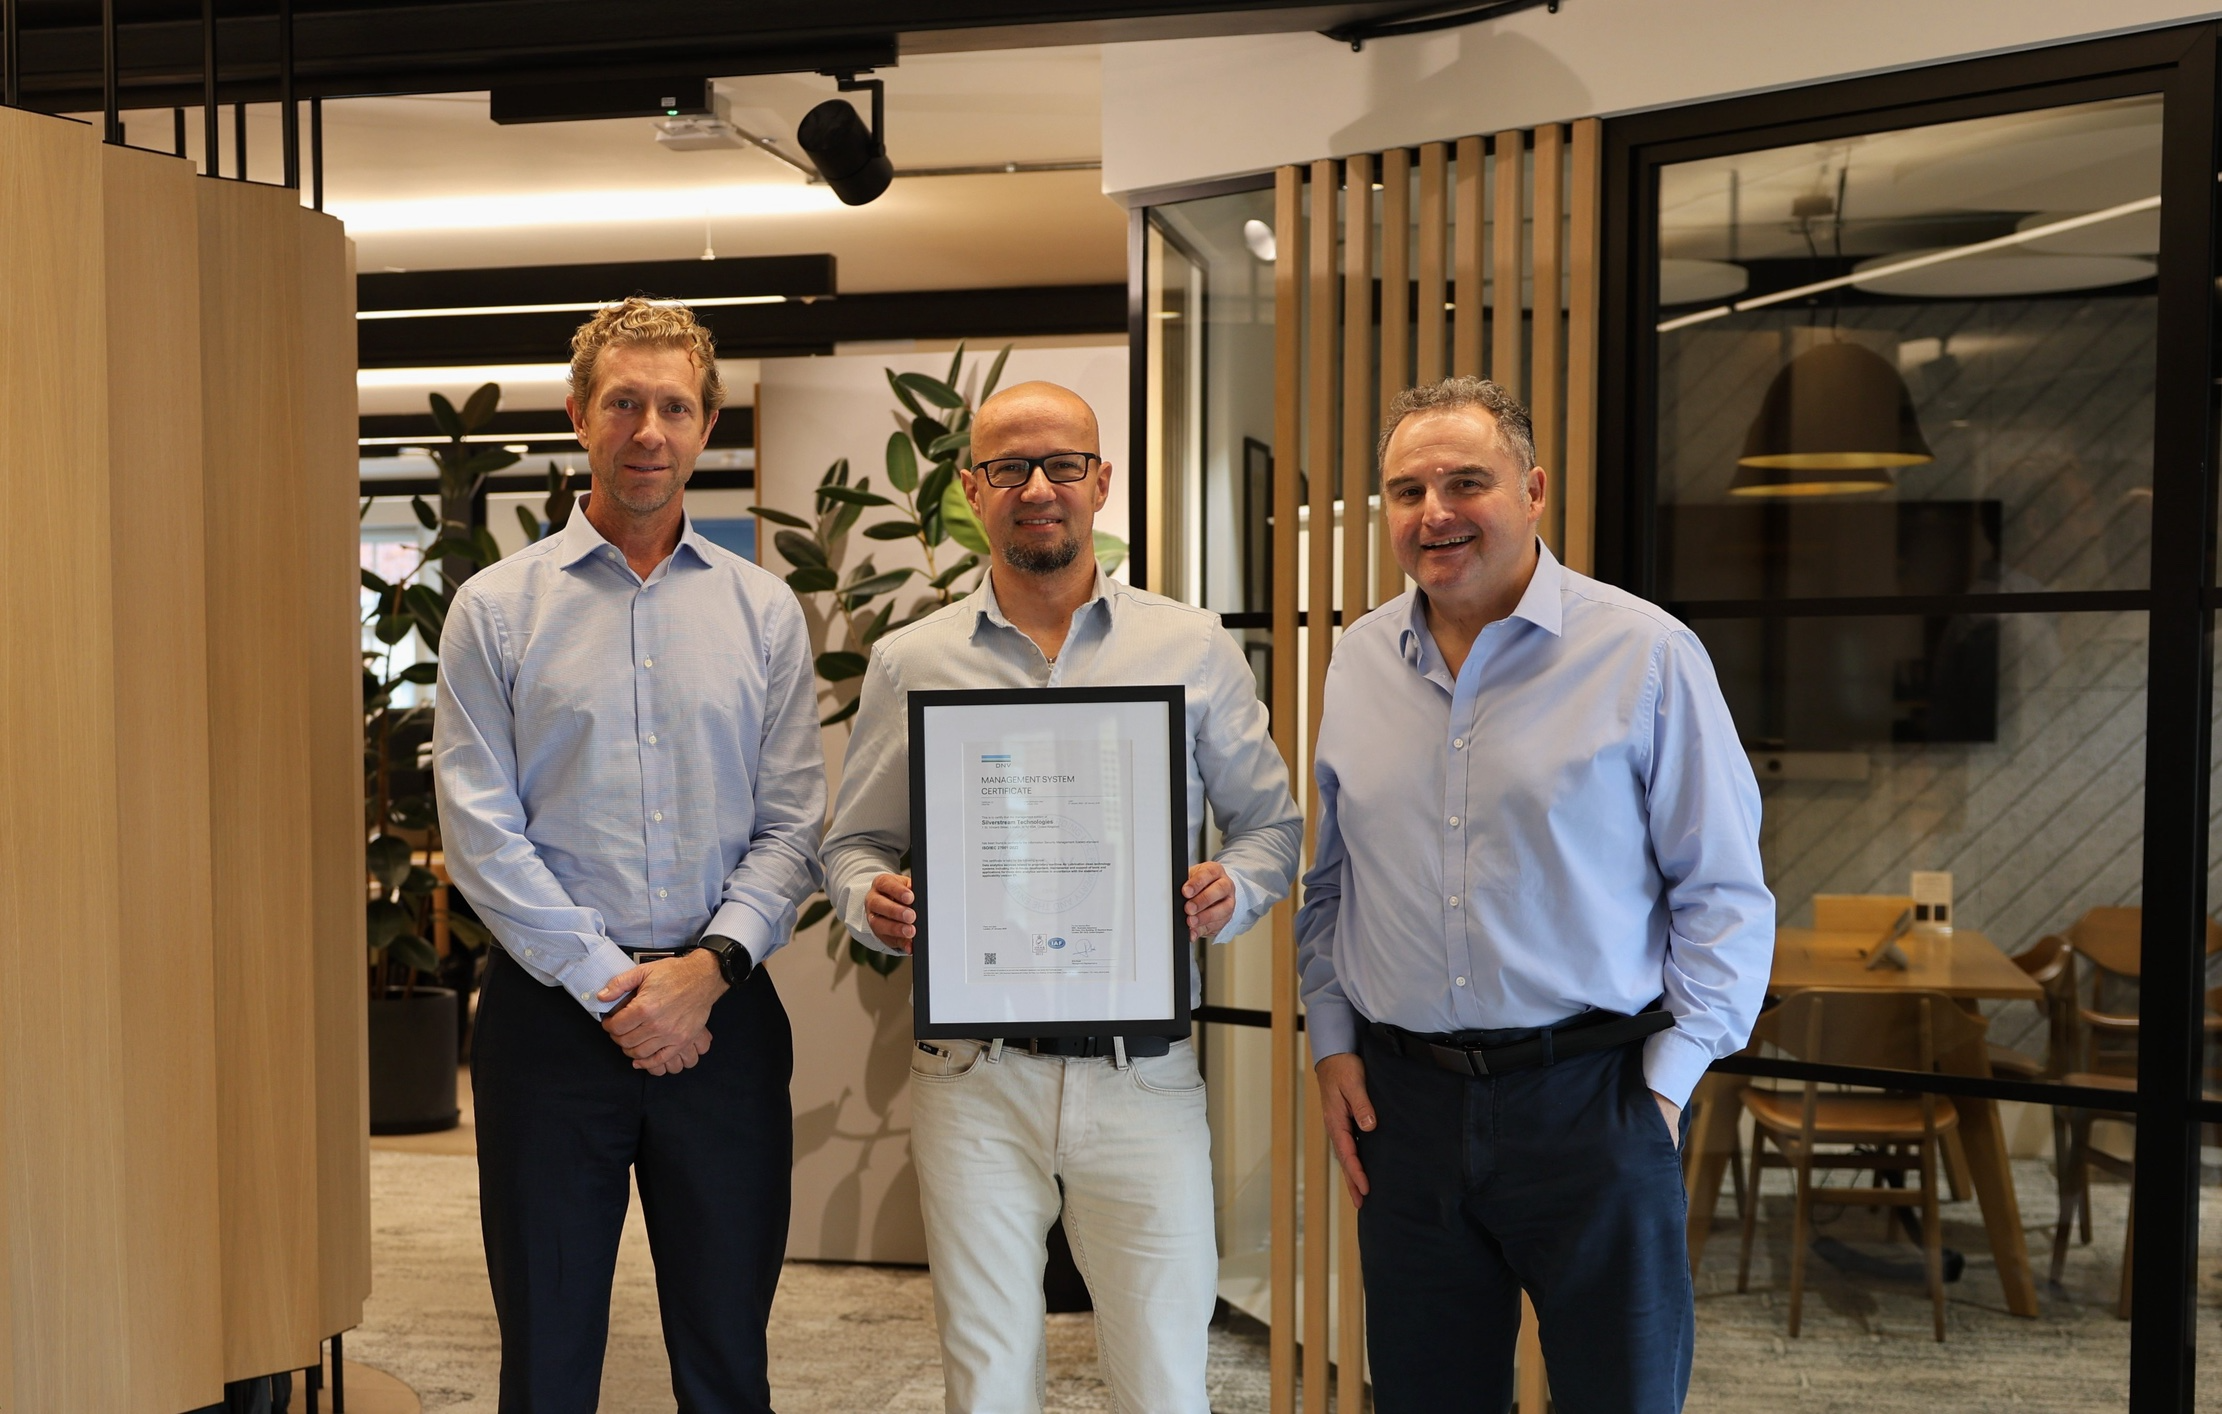
Silverstream, a market-leader in marine energy efficiency, has successfully extended the scope of its ISO 27001 certification following the completion of this year’s audit programme by leading classification society DNV.
Recognising sector-leading capability in how Silverstream manages the security of connected systems and customer data, the certificate applies to all three of the company’s sites, including its London headquarters, its Global Operations Centre (GOC) in Southampton and its Shanghai office. It also covers every internal function, including product development.
Silverstream’s technology increasingly connects vessels to shore, with more data and more digital services running across a growing fleet. The certificate reaffirms that every new digital capability Silverstream builds, from onboard control software to fleet performance analytics, is designed, developed and maintained under an information security management system that DNV audits independently.
Commenting on the announcement, Nick Chrissos, Chief Digital and Information Officer at Silverstream, said: “Information security has become a procurement question in shipping, not just an IT one. It’s a condition of doing business. Our customers trust us with systems that run on their vessels and data that shapes their commercial decisions.
“Extending ISO 27001 to product development means security is built into how we create technology from day one, not added at the end.”
This certification comes as cyber resilience moves firmly into class rules. IACS Unified Requirements E26 and E27 apply to ships contracted for construction from 1 July 2024, with UR E27 covering on-board systems and equipment supplied by third parties. Independent certification gives owners, yards and class societies a clear view of how a supplier governs its systems and data, from design through to in-service support.


